Azure change history, in plain English.

Somebody changed it. Nobody remembers who.

Every change in your Azure tenant, with the configuration before and after, kept past Azure's own 90-day and 14-day windows. Read-only. Set up in ten minutes.

Connect your tenant How it works

app.kronikl.io/timeline
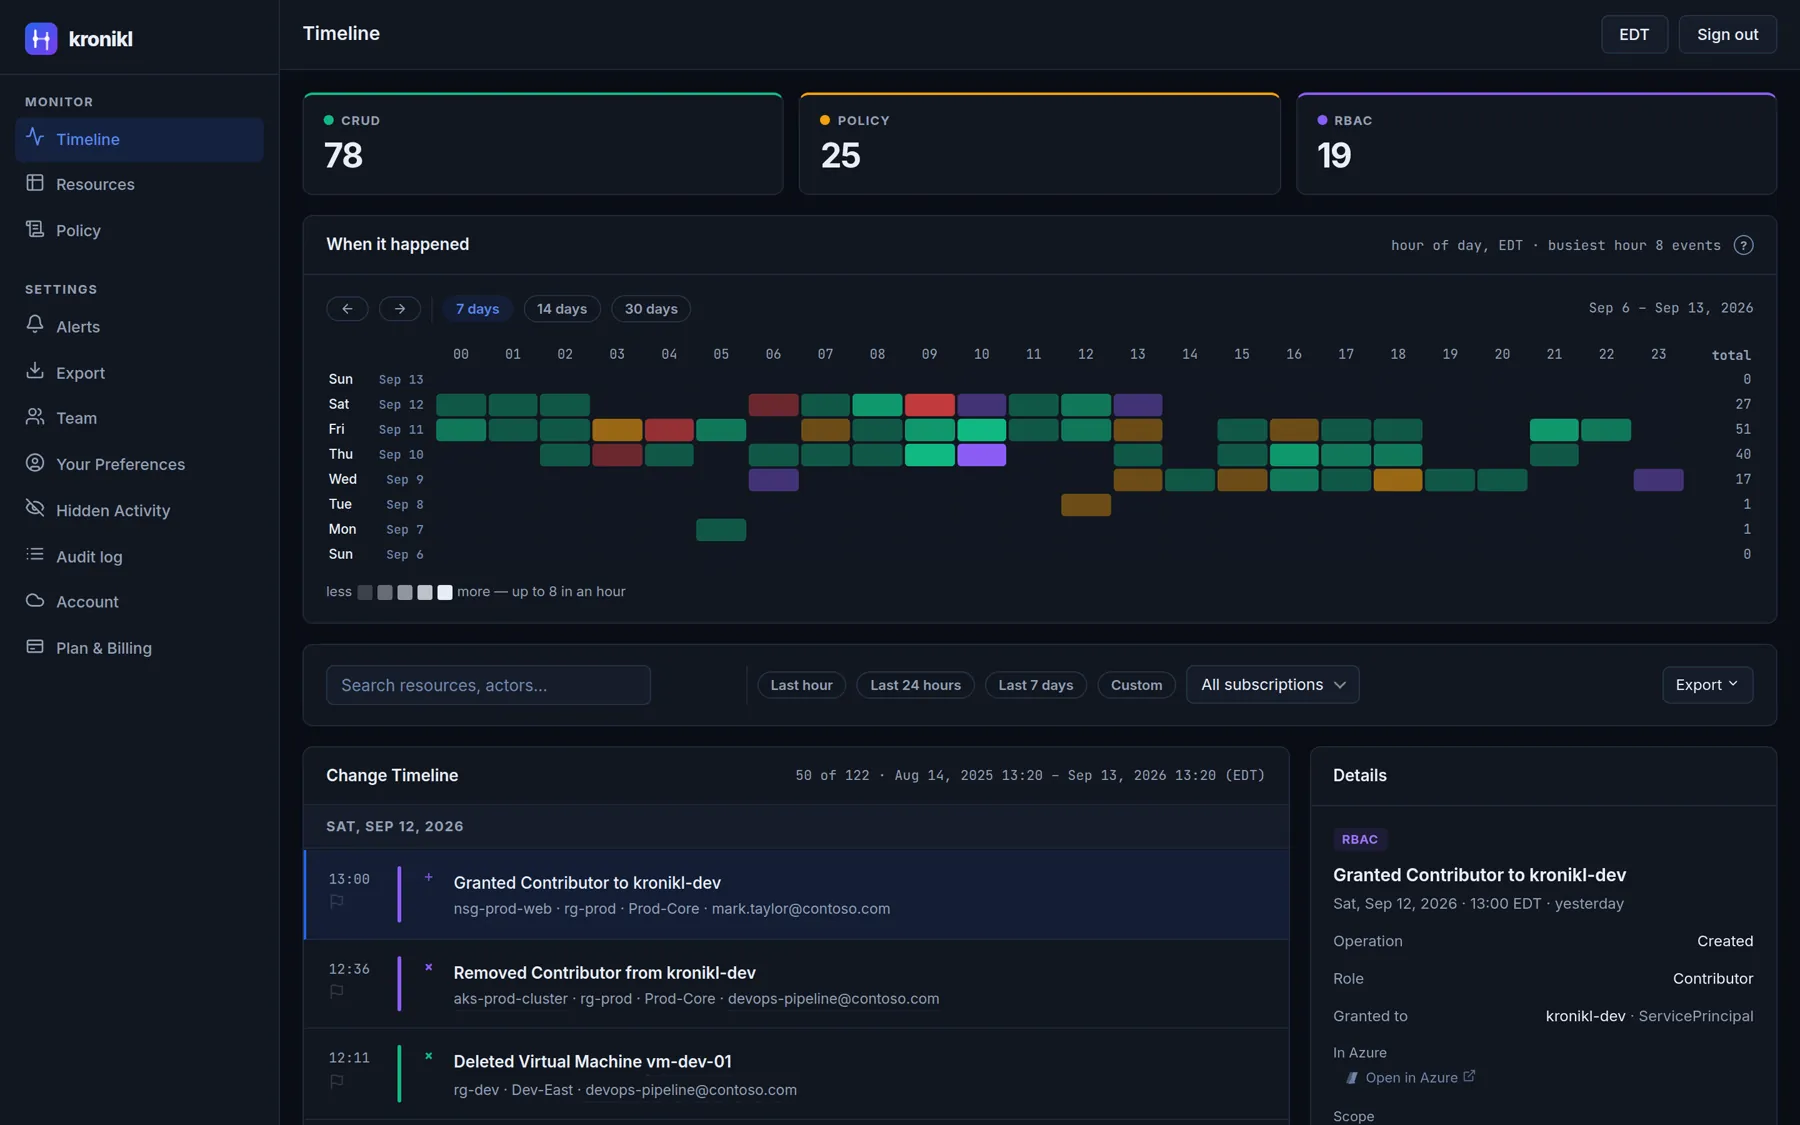
Kronikl's timeline screen: counters for CRUD, policy and RBAC changes; a heat map of when changes happened by hour and day; the change timeline with search and time filters, showing a Contributor role granted on nsg-prod-web; and a details pane naming the operation, the role, who it was granted to, the scope, and who performed it.

Azure shows what is running today. Kronikl shows what changed.

What the Azure Activity Log keeps

{
  "operationName": {
    "value": "Microsoft.Network/networkSecurityGroups/securityRules/write"
  },
  "eventTimestamp": "2026-09-06T21:52:37Z",
  "status": { "value": "Succeeded" },
  "category": { "value": "Administrative" },
  "caller": "mark.taylor@contoso.com",
  "resourceId": "/subscriptions/5f8e1d2c-…/resourceGroups/rg-prod/providers/
                 Microsoft.Network/networkSecurityGroups/nsg-prod-web/securityRules/allow-inbound",
  "authorization": { "action": "…/securityRules/write", "scope": "…/nsg-prod-web" },
  "correlationId": "4c1f0a6e-8d2b-4b3a-9f7e-2a5d6c8e1b03"
}
// no field carries what the rule was before, or after

Azure Monitor activity log event, shortened

What Kronikl keeps

CRUD Changed a network security rule

nsg-prod-web · rg-prod · Prod-Core · mark.taylor@contoso.com · Sep 6, 2026 · 22:52

A · Mon, Aug 17, 2026 · 03:23B · Sun, Sep 6, 2026 · 22:52
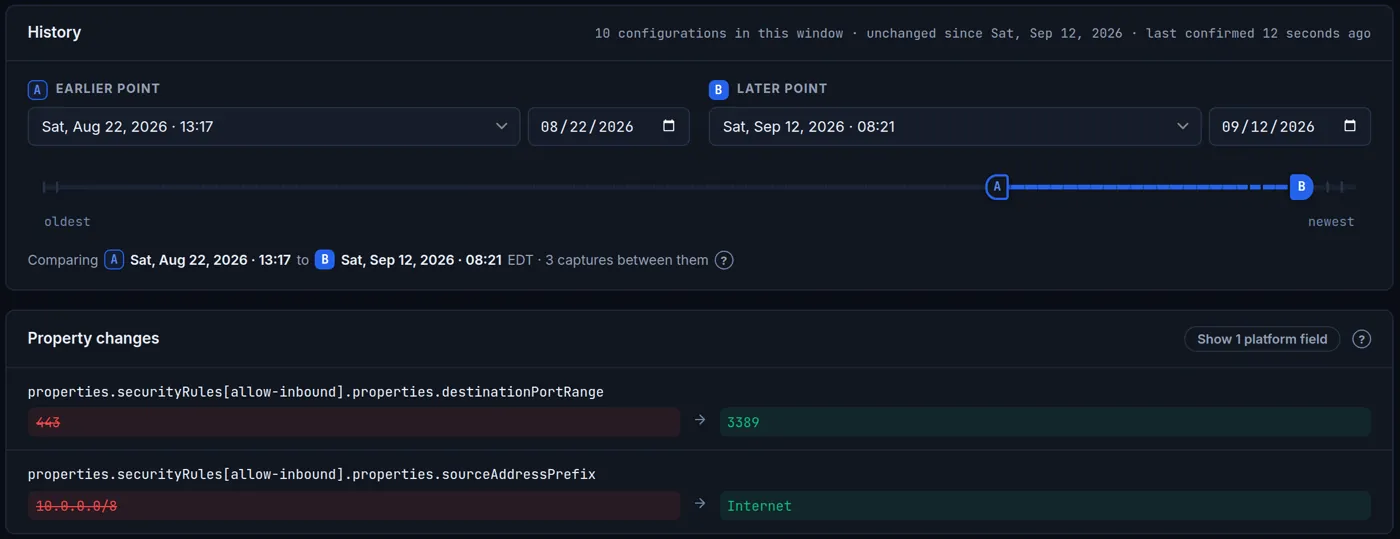
securityRules[allow-inbound].destinationPortRange 4433389
securityRules[allow-inbound].sourceAddressPrefix 10.0.0.0/8Internet
One of these tells you RDP was just opened to the internet.

The auditor is asking about March. The person who widened the NSG rule left in April.

Nothing to install.

  1. Admin consent, in the browser

    A Global Administrator approves three read-only Graph permissions, and two delegated scopes used only while you are signed in.

  2. An Azure RBAC role, granted by you

    Give Kronikl Azure's built-in Reader role at the subscriptions or management groups you pick: one click with your own sign-in, or a command for CLI, PowerShell, Terraform or Bicep.

  3. Recording starts

    Kronikl records everything it can see, then watches on a schedule. New changes appear within minutes.

What you can see

Who changed this Azure resource, and when

One feed of every change: resources, policy and role assignments. Filter by anything on the row. No query language.

  • Every administrative write, including the denied and failed ones.
  • Routine platform events hidden by default, one click to show.
  • Every filter lives in the URL, so a view is a link you can paste into a ticket.

Configuration drift, side by side

Pick any two points in a resource's history and see which properties differ, by path.

  • Walk back through every snapshot until the setting was right.
  • Fields Azure rewrites on its own are folded away. Add one NSG rule and you see one added rule, not twelve moved ones.
  • A to B and back to A is a revert, and all three snapshots are kept.
The History and Property changes panels for nsg-prod-web: a scrubber between an earlier snapshot on August 22, 2026 and a later one on September 12, 2026, and two changed properties — the allow-inbound rule's destination port range from 443 to 3389, and its source address prefix from 10.0.0.0/8 to Internet — with one platform field folded away.

An export your auditor can use

The whole date range as CSV or JSON, streamed, no row cap. Any comparison copies out as plain text with both content hashes, when the state was last confirmed, and what it cannot tell you.

  • Includes the routine events the timeline hides, with routine as a column.
  • Every row says where the fact came from and when. A clamped range says so.
  • An auditor's account scoped to one subscription or resource group exports only that.
Kronikl — configuration diff

Resource      /subscriptions/5f8e1d2c-…/networksecuritygroups/nsg-prod-web
Type          microsoft.network/networksecuritygroups
Before        2026-08-17T02:23:07.247Z (UTC)  d750a0b4…6749e07
After         2026-09-06T21:52:37.247Z (UTC)  32dc7d4f…c4ed4
Confirmed     2026-09-06T21:52:37.247Z (UTC) — NOT confirmed since, 2 day(s) ago
Window        21 days
                These are the nearest snapshots either side of the change, so the
                differences below cover the whole window and not a single operation.

Changes (2)
  properties.securityRules[allow-inbound].properties.destinationPortRange
    before: 443
    after:  3389
  properties.securityRules[allow-inbound].properties.sourceAddressPrefix
    before: 10.0.0.0/8
    after:  Internet

1 platform field(s) also differ and are not listed — Azure changes these on its own.

Events in this window (21)
  2026-09-04T06:36:07.247Z  networksecuritygroups created — nsg-prod-web — devops-pipeline@contoso.com
  2026-09-04T07:54:07.247Z  networksecuritygroups modified — nsg-prod-web — mark.taylor@contoso.com

Rules that watch for what you would otherwise find later

Set a rule: a privileged role granted, a production resource deleted, an NSG opened to the internet, a policy assignment removed. Matches are grouped, so a burst is one finding, shown in the app.

Reader, granted by you, and checked by a read

This is what connecting your tenant grants.

  • Read-only, always

    Azure's built-in Reader role. It cannot write or delete.

  • You grant it

    Create the role assignment shows you the role, the principal and the scopes, then makes the grant with your own Azure sign-in. Or take the command and run it yourself.

  • Nothing stored

    No secret, password or API key against your tenant. Withdraw consent in Entra and the next token request fails.

How Kronikl compares

If you already have a SIEM

Your SIEM Kronikl
Who it is for
A SOC analyst Whoever administers the tenant
Query language
KQL, and rules to maintain Filters and a URL
Point-in-time config diff
Not what log search is for Property-level diff between any two snapshots

If you are weighing an audit suite

An audit suite Kronikl
Scope
AD, file shares, on-premises, Azure Azure only
Getting started
Agents, collectors, a project Admin consent and one role assignment
Commitment
An annual contract A free plan

Start on Pro, stay free after the trial if it fits.

Two weeks on Pro. Nothing is deleted when a plan narrows, so upgrading restores the older history the same day.

Free

$0/month

  • 14 days of queryable history, at one scope
  • The full timeline, diff, resources and export
  • Alert rules, and their findings in the app
  • Unlimited team members from your tenant
Connect your tenant

Questions before you sign up

Where is my data stored?

In the United States, on Microsoft Azure. Azure encrypts managed database storage at rest by default, and everything is served over TLS.

What happens to my data if I stop using Kronikl?

Close your account from inside Kronikl and we delete everything within seven days, then confirm by email. If you stop signing in, nothing is deleted until you ask. Stopping collection for one tenant keeps its history readable and exportable.

Stop guessing what changed.

Recording starts within minutes of connecting.

Connect your tenant See what it can reach